


An asset can disappear from production and still fail disposition. A server is offline, but its storage media has no sanitization record. A device left the building, yet nobody can match the carrier scan to its serial number. A VM was terminated while its snapshots and support contract stayed behind.
IT asset disposition (ITAD) is the controlled process of retiring unwanted IT equipment and storage media through approved reuse, resale, recycling, return, or destruction. It covers data sanitization, chain of custody, final destination, and the records that prove each action took place.
In hybrid environments, the same retirement decision may also trigger cloud decommissioning and software license reclamation. These are related workflows, but they require different controls and evidence.
This guide follows the record an ITAM lead must close: asset identity, ownership, approval, dependencies, sanitization, custody, software obligations, and final reconciliation.
TL;DR
- Five control gates: Register and authorize the asset, remove it from service, sanitize and validate media, track custody, and reconcile records before closure
- Data sanitization: Apply NIST SP 800-88 Rev.2 Clear, Purge, or Destroy methods based on media characteristics, data sensitivity, and intended destination
- Chain of custody: Match asset identifiers to transfer records, receiving facilities, and final disposition evidence
- Audit-ready closure: Verify approvals, sanitization results, software and contract actions, and inventory updates before marking the case closed
- CMDB support: Helps teams review asset ownership, dependencies, change history, and configured disposition records without replacing physical ITAD providers
What is IT asset disposition (ITAD)?
IT asset disposition is the governed handling of IT equipment and storage media that an organization no longer needs. It begins with an approved retirement decision and ends when the asset reaches its authorized destination, sensitive data has been handled appropriately, and the inventory and financial records reflect the outcome.
ITAD primarily applies to physical equipment such as servers, storage arrays, network devices, laptops, removable media, and data center components. Depending on condition, ownership, and risk, an asset may be redeployed internally, returned to a lessor, resold, donated, recycled, or destroyed.
Cloud resources and software require adjacent closeout activities. Snapshots, unattached volumes, machine images, service accounts, SaaS subscriptions, and license entitlements can remain active after their associated workload or hardware is retired. They should be reconciled within the same retirement case where relevant, but deleting a cloud resource is not proof that physical storage media was sanitized.
A complete information technology asset disposition record answers four questions:
- What asset was retired, and what data did it contain?
- Who approved its disposition route and performed the required controls?
- What evidence confirms sanitization, custody, and final destination?
- Were related infrastructure, software, contracts, and financial records reconciled before closure?
When any answer is missing, the asset may be out of service without being fully dispositioned.
IT asset disposition vs disposal, retirement, and software disposition
These terms describe different activities at the end of an asset's lifecycle. Confusing them creates gaps between technical retirement, physical handling, and financial closure.
| Process | Definition | Scope and activities | Evidence of completion |
|---|---|---|---|
| IT asset disposition (ITAD) | Controlled end-of-use management of physical IT equipment and storage media | Approval, sanitization, custody tracking, reuse, return, resale, recycling, or destruction | Approved route, sanitization result, custody history, final receipt, reconciled records |
| IT asset disposal | Physical removal or final handling of equipment no longer needed | Equipment collection, transfer to a recycler or buyer, return, donation, or destruction | Transfer records, recipient confirmation, recycling or destruction documentation |
| Asset retirement | Removal of an asset or CI from its operational role | Dependency checks, change approval, workload migration, lifecycle status updates | Approved change request, dependency sign-off, updated CI status |
| Software disposition | Reclamation, reassignment, or termination of software rights and obligations | License recovery, entitlement reassignment, subscription cancellation, contract updates | Usage validation, entitlement action, contract or renewal confirmation |
| Cloud resource decommissioning | Controlled removal or archival of cloud resources and their dependencies | VM termination, snapshot cleanup, storage removal, identity revocation, backup review | Provider state, dependency checks, deletion or archival records |
A CI marked Retired does not prove that its physical media was sanitized. Similarly, a server returned to a leasing company may still have software obligations associated with its former installation.
For the broader lifecycle and retirement decision, see IT Asset Lifecycle Management.
Enforce required CI attributes such as
data_classification,disposition_method, andvendor_id. Auditors often check these fields to verify the completeness of your chain of custody. Missing data in these fields usually means incomplete proof.Kristina, Senior ITAM expert at Cloudaware
The IT asset disposal process: five control gates
A structured IT asset disposal process should define what must happen, who is responsible, and what evidence permits the asset to move to the next stage.
The same basic workflow can apply to a laptop or a batch of 300 data center servers. Scale changes the logistics and reconciliation effort, but not the control requirements.
| Gate | Required action | Evidence and pass condition |
|---|---|---|
| 1. Register and authorize | Confirm asset identity, owner, data classification, dependencies, and proposed disposition route | Approved request with named owner, approver, and asset identifier |
| 2. Remove from service | Stop workloads, revoke access, transfer required data, and check dependencies | Change record and owner confirmation that removal will not cause unapproved impact |
| 3. Sanitize and validate | Select and execute an appropriate method for the media and its destination | Sanitization result, verification, and accepted validation decision |
| 4. Transfer to the final route | Redeploy, return, resell, donate, recycle, or destroy the equipment under controlled custody | Item-level handoffs and confirmation that expected and received assets match |
| 5. Reconcile and close | Update inventory, software, contracts, financial records, and evidence references | No unresolved evidence gaps or unapproved dependencies remain |
Disposition planning should identify a proposed route before sanitization because the next destination affects the required method. The route can change if sanitization fails, the equipment is damaged, or the recipient cannot meet the required conditions.
Batch work also requires count reconciliation. Track how many assets were expected, collected, received, sanitized, and finally processed. If a recycler receives 299 of 300 expected servers, the missing serial number must remain an open custody exception.
For the broader workflow before disposition, read IT Asset Management Process: 6 Workflow Steps You Can't Ignore.
1. Build the disposition record before the asset moves
Without clear ownership and asset disposition management, even the best IT asset disposal process can fail. Someone must decide when an asset is retired, who approves the change, and who signs off on the data's removal.
In large environments, responsibility is often split: ITAM tracks inventory, Security defines sanitization requirements, GRC reviews compliance evidence, and Operations handles the technical work.
This way, the same asset can appear in four systems, each with a different status.
The first control is to establish a consistent disposition record linked to the asset's CI. The record should connect the retirement decision with any relevant change request, sanitization event, custody transfer, financial action, and final receipt.
At minimum, capture:
- Identity: Asset tag, serial number, CI ID, device or media type, and current location
- Business context: Service or application, business owner, technical owner, and cost center
- Risk: Data classification, legal hold status, encryption state, and media condition
- Dependencies: Related CIs, workloads, backups, snapshots, identities, and open incidents
- Commercial status: Ownership or lease, warranty, support contract, and remaining book value
- Disposition decision: Proposed route, sanitization requirement, approver, executor, and case ID
The same identifier must follow the asset across systems. If a pickup record contains a pallet number but no reference to the underlying device serial numbers, it may not be possible to demonstrate which equipment reached the facility.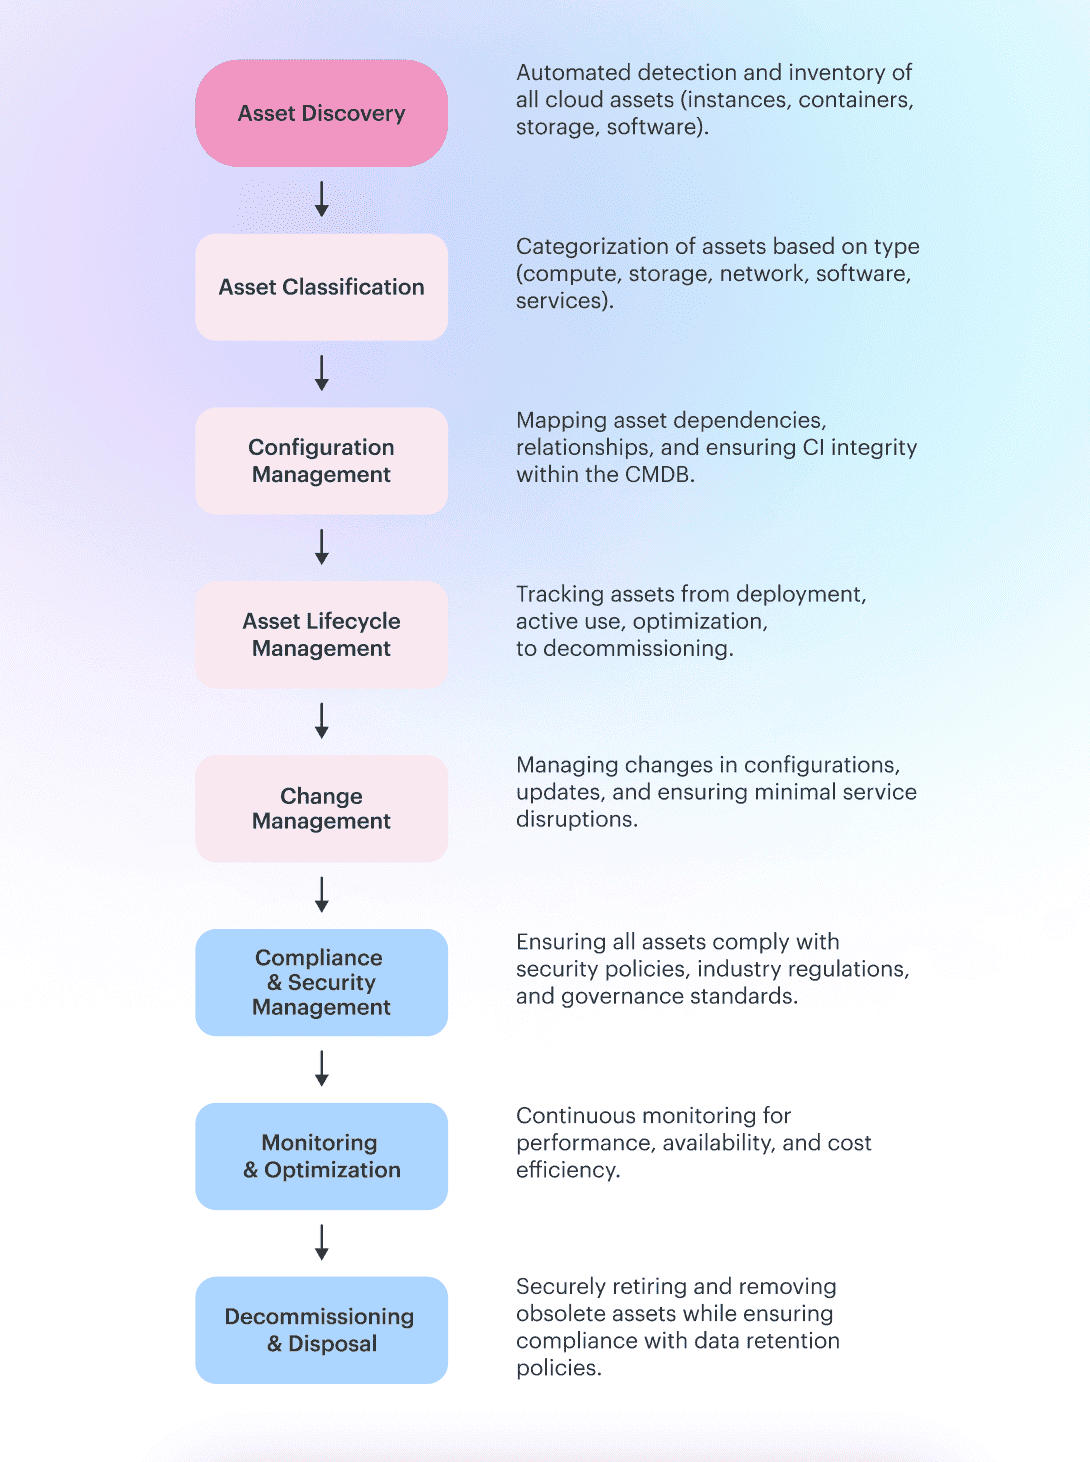 IT asset lifecycle from discovery and configuration management to decommissioning and disposal
The best practice is to document this flow as part of the asset management and disposal policy:
- Who initiates retirement. Usually the service owner or application team, after confirming that the asset is no longer needed
- Who approves. The authorized owner approves the disposition decision, while Security defines the sanitization requirements and GRC reviews policy exceptions where applicable
- Who executes. Operations or Cloud Operations performs decommissioning, media sanitization, and the necessary handoffs
- Who verifies and closes. ITAM reconciles the disposition record; GRC or another designated reviewer examines evidence where the policy requires it
This flow must be policy-driven, not personality-driven. The required fields, approvals, and evidence should remain consistent regardless of which team performs the work.
Consider a leased storage appliance that contained customer data. The service owner confirms that dependent workloads have been migrated. Security approves a suitable sanitization technique for returning the appliance to its lessor. Operations records the result, and the receiving party confirms the serial number.
If sanitization validation fails, the asset cannot progress to the return stage under the original plan. The case remains open while the team repeats sanitization, escalates to another method, or negotiates an approved alternative with the lessor.
How Cloudaware helps with ownership and control
Cloudaware configuration items can provide the asset identity, ownership metadata, related infrastructure, and history needed for the initial review.
Role-based permissions and configured approval workflows can support the governance process. Where Jira or ServiceNow integrations are implemented, teams can use CI identifiers and relevant context when coordinating disposition tasks.
The specific approval, synchronization, and state-transition rules depend on the customer's configuration. A CMDB lifecycle status should not be treated as proof that an external sanitization or disposal activity took place.
Read also: 9 Parts of IT Asset Management Policy That Works for Hybrid Setup.
2. Sanitize media and control the handoff
Secure data handling sits at the core of any information technology asset disposal program. You cannot demonstrate that a device was handled according to policy without knowing what data it held, which sanitization method was selected, and whether the result was accepted.
The relevant reference is NIST SP 800-88 Rev.2, published in September 2025. The revision places greater emphasis on an organizational media sanitization program and decisions based on confidentiality requirements, media characteristics, control of the equipment, and intended reuse.
Select the sanitization method
NIST describes three primary sanitization methods:
- Clear: Logical techniques that protect against simple, non-invasive recovery using the normal device interface
- Purge: Logical or physical techniques intended to make recovery infeasible using state-of-the-art laboratory methods while potentially allowing media reuse
- Destroy: Techniques that render the media incapable of storing data and make target-data recovery infeasible
The correct method depends on the media, the confidentiality of the information, the intended destination, and the assurance available from the selected technique.
A functioning laptop approved for internal redeployment, a storage array returning to a lessor, and a damaged SSD leaving organizational control may require different sanitization decisions.
One important distinction in Rev.2 concerns degaussing. It can be an applicable physical Purge technique for certain magnetic media, but it is not a Destroy method. It must not be applied indiscriminately to modern storage devices, especially flash-based media.
Verify execution and validate the result
Sanitization should produce a record of the technique used, the operator, the date, the tool and version where applicable, and the outcome.
NIST SP 800-88 Rev.2 distinguishes two assurance activities:
- Verification checks whether the selected technique completed successfully. For example, the operator may inspect the tool's completion status and any reported errors.
- Validation determines whether the result is acceptable for the confidentiality requirements and intended destination. A successful tool operation does not automatically mean the result meets the organization's policy.
If validation is rejected, the media must follow an approved corrective path, such as repeating sanitization with another technique or escalating to a stronger method.
NIST provides a sample Certificate of Sanitization in Appendix C. Its fields are useful when designing internal forms or reviewing vendor documentation. The completed certificate must still correspond to the actual media and work performed.
Maintain a verifiable chain of custody
Once equipment moves between teams, buildings, carriers, or processing facilities, every handoff should be traceable.
The custody record should include the asset or media identifier, sender, receiver, timestamp, location, carrier or facility, and any relevant seal or container reference.
For data center batches, reconcile individual serial numbers wherever the control requires item-level traceability. A pallet-level receipt alone does not necessarily prove that each device was received and processed.
Choose the final disposition route
The route should be proposed during planning and confirmed against the asset condition, sanitization outcome, contractual obligations, and recipient requirements.
| Route | When it makes sense | Required closure evidence |
|---|---|---|
| Internal redeployment | Equipment is functional, supported, and approved for another use | Sanitization or reconfiguration record, new owner, updated CI |
| Return to lessor or manufacturer | Ownership or contract requires the return | Return authorization, sanitization decision, carrier and recipient confirmation |
| Resale or donation | Equipment is reusable and transfer is permitted | Sanitization validation, condition or test result, recipient receipt |
| Recycling | Reuse is no longer viable and material recovery is appropriate | Facility receipt, asset reconciliation, applicable recycling documentation |
| Destruction | Media condition, confidentiality risk, or policy rules out reuse | Destruction method, corresponding item or batch evidence, certificate reference |
External ITAD providers require their own due diligence.
Under R2v3, a facility's general certification does not establish that every specialized sanitization activity is covered. SERI's specialty process requirements explain the enhanced controls in Appendix B, including physical and logical sanitization.
The e-Stewards Standard addresses downstream due diligence and incorporates NAID AAA certification requirements for certified processors. i-SIGMA's NAID AAA program provides independent verification of secure destruction operations.
Check that the actual receiving facility holds a current certification covering the service being purchased. Also establish which downstream facilities will handle the equipment and what proof each stage will produce.
Check digital dependencies before closure
Before a retiring asset's case is closed, confirm that related cloud resources and technical dependencies have been accounted for.
A decommissioned server may leave behind backup copies, object storage buckets, snapshots, monitoring configuration, service accounts, or encryption keys. Some must be removed, while others may require retention or reassignment.
The pass condition is not necessarily zero remaining related objects. It is that no unresolved dependency remains without an accountable owner, approved treatment, or documented exception.
3. Reclaim licenses and software after asset disposal
The process of disposing of assets involves more than hardware. Associated licenses, contracts, and support subscriptions may need to be reclaimed, transferred, or terminated when a server, database, or application is no longer in use.
A retired database server may still carry an operating-system subscription, backup agent, monitoring license, maintenance agreement, and cloud capacity commitment. If these obligations are not reviewed, costs can continue after the technical asset is gone.
That is why software disposition needs a separate closeout track linked to the retirement case.
A practical software and license reclamation process includes:
- Discovery and mapping: Identify installed software, subscriptions, contracts, and entitlements associated with the retiring CI
- Usage validation: Confirm whether another workload, user, or host still depends on the software
- Reclamation: Reassign transferable rights, remove unnecessary seats, or terminate eligible subscriptions
- Financial reconciliation: Confirm that purchasing, renewal, and cost records reflect the completed action
An installation count alone is insufficient. Software may disappear from a host while the subscription remains active, or a license entitlement may remain valid and transferable after the original device is retired.
Common problems include:
- SaaS accounts remaining licensed long after user offboarding
- Database support agreements renewing after decommissioning
- OS and backup licenses being overlooked within enterprise agreements
- Paid subscriptions remaining active after teams move to alternative services
The ITAM or Software Asset Management owner should determine whether each right must be kept, reassigned, terminated, or escalated for contract review.
The closure record should retain the relevant license or contract identifier, usage decision, action date, new assignee where applicable, and confirmation from the authoritative entitlement or purchasing system.
Treat license reclaim as part of the same ITAD approval chain. The same ticket that triggers sanitization should also trigger reclaim. Use tagging or linkage (
license_sku_idorentitlement_id) to connect every software asset to its host CI. This creates traceability between hardware and financial cleanup.Mikhail Malamud, Cloudaware GM
How Cloudaware helps with software disposition
Where relevant integrations or agents are configured, Cloudaware can provide discovered software inventory and infrastructure context linked to CIs. This gives ITAM teams a starting point for identifying software associated with assets marked for retirement.
Custom attributes, relationships, and reports can help organize the review. However, license entitlement validation, contractual transfer rights, termination, and financial reconciliation depend on the customer's authoritative software and purchasing systems.
The resulting information can support FinOps reporting where the necessary billing and business data is available. Reclaimed savings should be confirmed against actual contract or billing changes, rather than inferred from an updated CI status.
For the broader software asset management model, see What Is Asset Management Software? ITAM Pro Explanation.
4. Close the record with audit-ready evidence
The final stage of IT asset disposal is all about proof.
By this point, the equipment should have reached its authorized destination, the required sanitization work should be complete, and associated software and financial records should have been reviewed.
But until the evidence is reconciled and accepted, the disposition case is not fully closed.
A team may retire a server but fail to obtain the final recipient confirmation. Another may sanitize a drive without recording the method or the validation decision. In both cases, the underlying activity may have occurred, but the available records do not demonstrate completion.
A proper closeout evidence set usually includes:
- Approval record: Named approver, decision, timestamp, and any authorized exception
- Sanitization proof: Method, technique, tool or operator details, verification, and validation
- Pickup and logistics: Asset identifiers, custody transfers, carriers, and receiving facilities
- Final destination: Recycling, return, resale, redeployment, or destruction documentation
- Before-and-after inventory: Reconciliation of the original asset population against the outcome
- License and contract closure: Reassignment, cancellation, renewal adjustment, or documented exception
- Financial reconciliation: Updated fixed-asset records, proceeds, fees, or outstanding obligations where applicable
The evidence should refer back to the same asset and disposition case.
Run a closure check before sign-off
A record marked Closed is not sufficient when required evidence is missing.
Configure the CMDB, ITSM, or reporting system to identify disposition cases with incomplete fields or unresolved relationships.
For example, a closure report could return records where:
- Lifecycle status is Closed, but no final route is recorded
- Sanitization is required, but verification or validation is missing
- Equipment was transferred, but the final recipient is unconfirmed
- A dependency remains active without an approved owner or exception
- License or contract actions remain unresolved
- Required evidence references are absent
The expected result is no unresolved exceptions. Where policy permits closure with an exception, retain its approval, owner, rationale, and review or expiration date.
Evidence retention should follow applicable legal, regulatory, contractual, privacy, litigation-hold, and internal records-management requirements. There is no universal three-year or seven-year ITAD retention period.
The record should also preserve the relevant policy or rule version. An auditor reviewing historical disposition work needs to understand which requirements applied when the decision was made.
Read also: IT Asset Management Audit for Hybrid Setup: 9-Step Checklist.
ITAD example: retiring a VMware host during data center consolidation
Consider an ITAM team retiring a VMware ESXi host after its workloads have been migrated to another cluster. The server is powered down, but several questions remain: Were all dependent workloads moved? Who authorized its removal? Have the local drives been sanitized? Can the team prove that the disposal vendor received the equipment?
The disposition case needs to connect the infrastructure record with the physical disposal process.
The team starts in Cloudaware CMDB, locating the host through CMDB Navigator and reviewing its owner, application context, and Related CIs. If a virtual machine still appears associated with the retiring host, Operations checks whether the relationship reflects an unresolved dependency or outdated inventory data before approving removal.
Next, the team connects the CI to the retirement approval. Cloudaware's Change Management view provides recorded changes and, where configured, approval history. The associated Jira or ServiceNow request can carry the execution tasks and required sign-offs.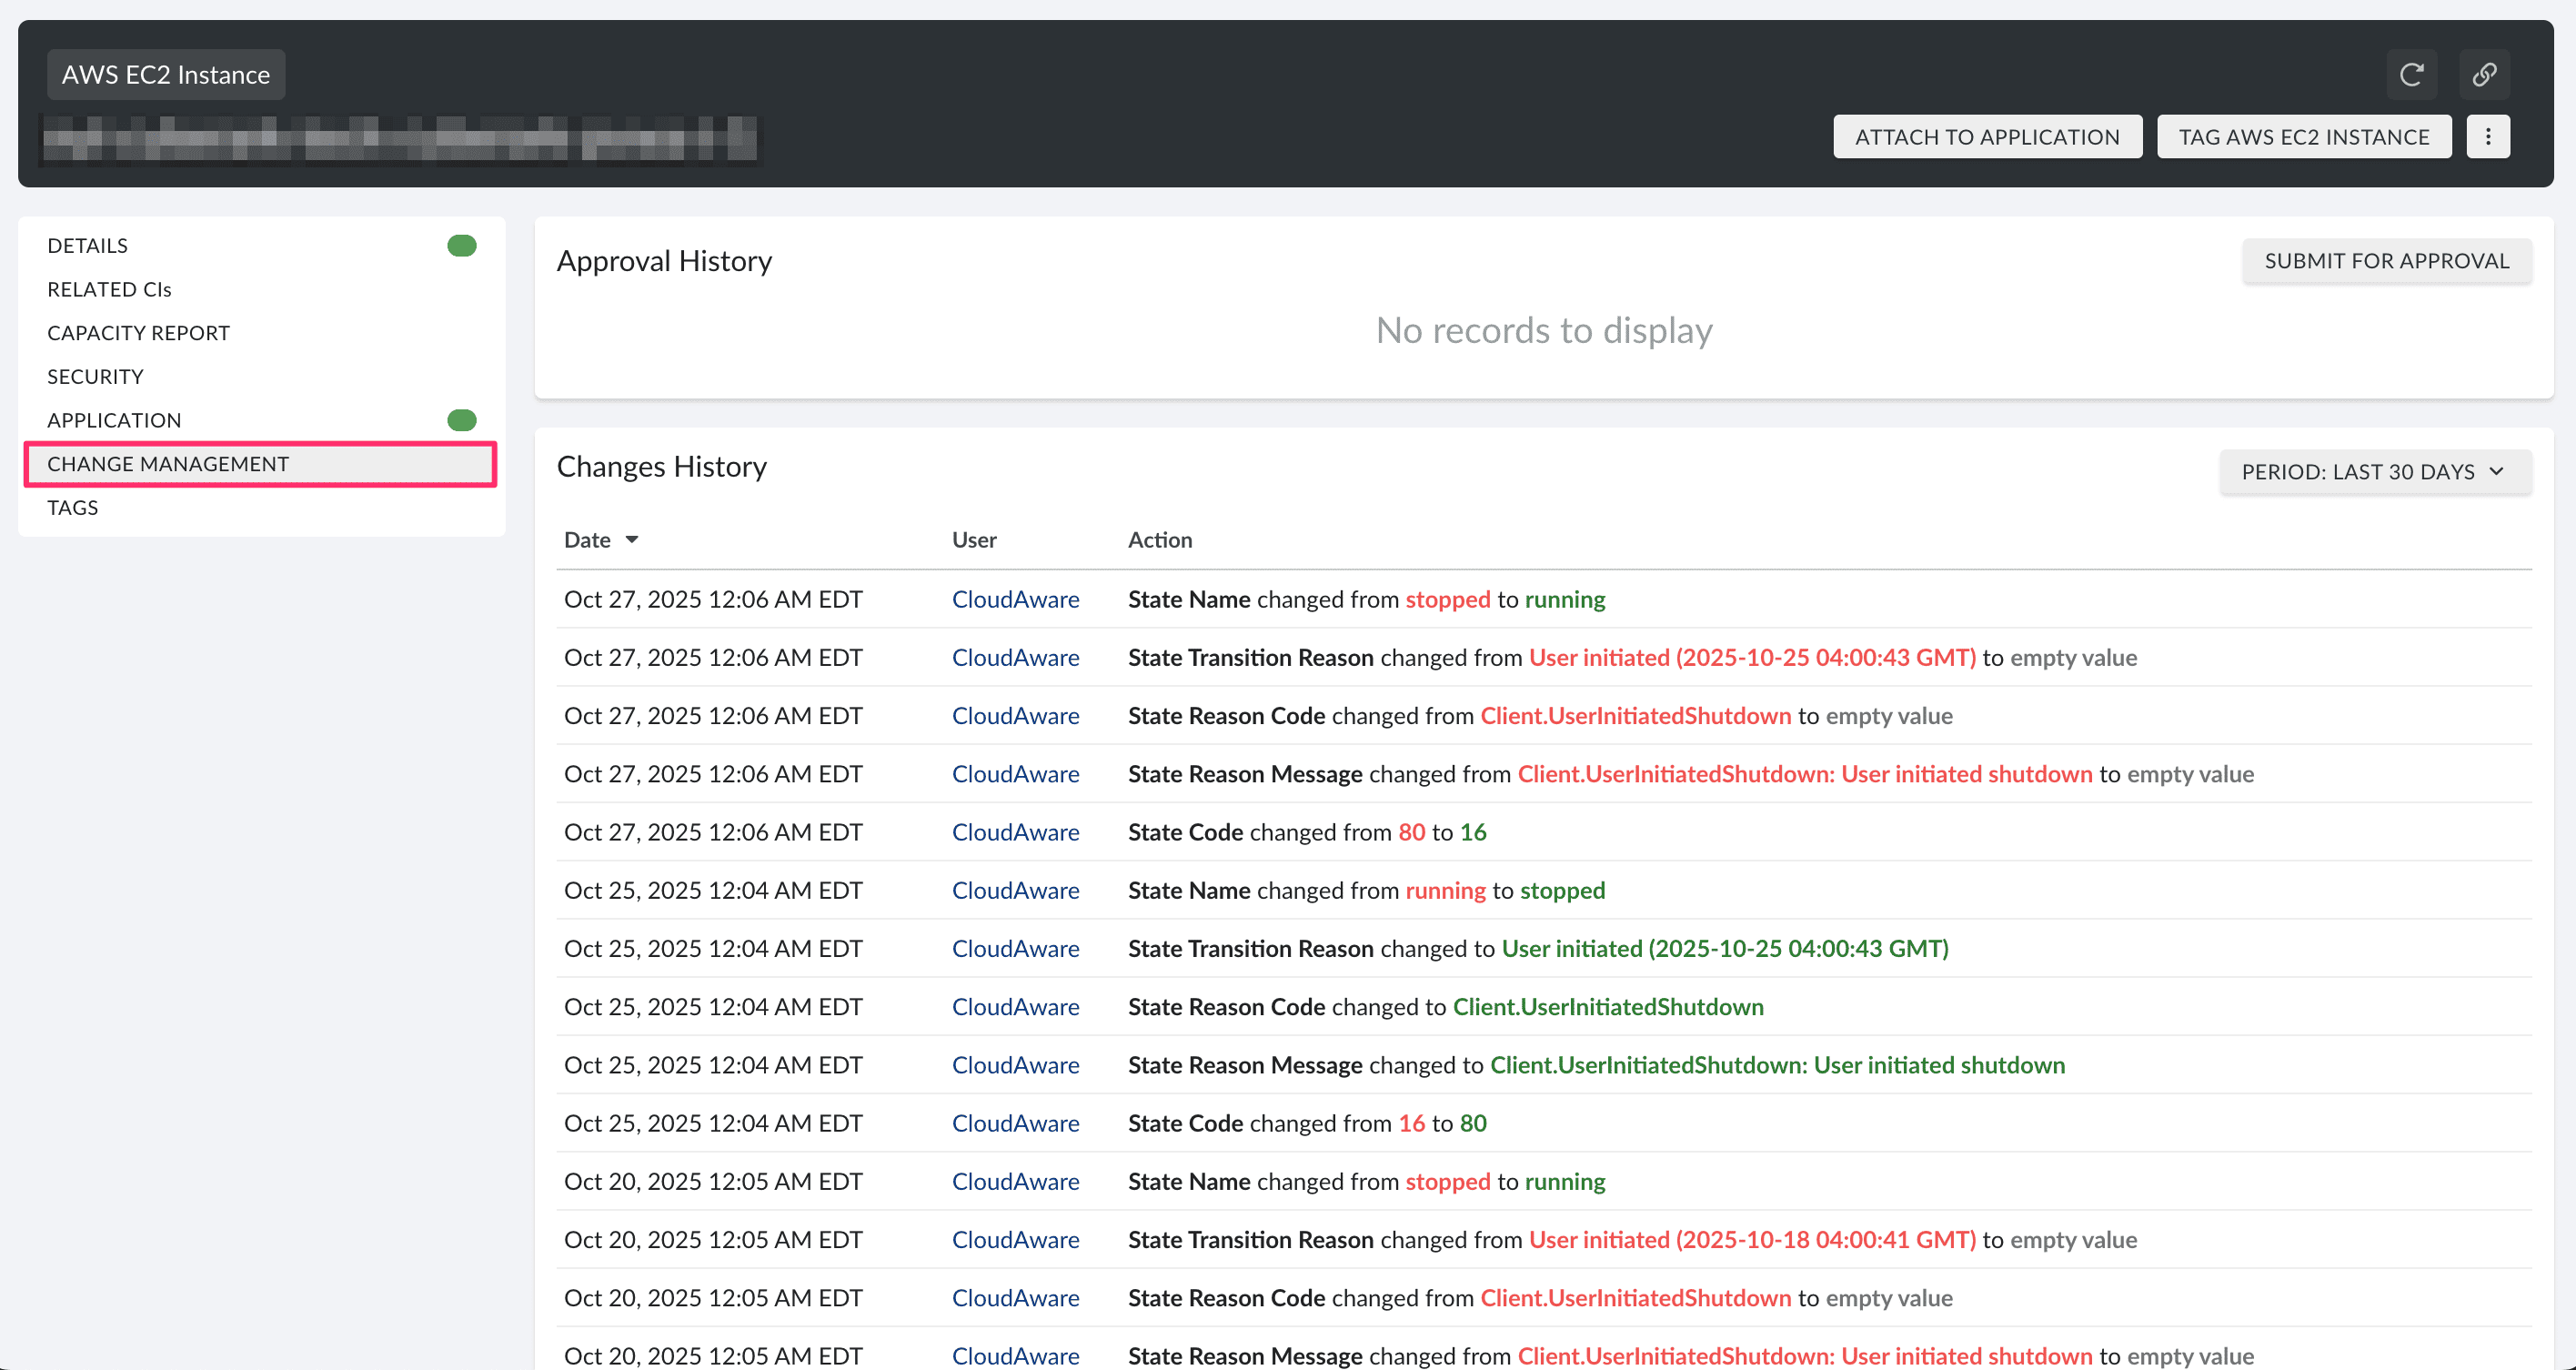 Cloudaware CI Change Management view showing Changes History and the Approval History panel.
The physical disposition happens outside the CMDB. The ITAD provider sanitizes the drives, records custody transfers, and issues the appropriate documentation. The team can configure disposition-specific fields in Cloudaware to reference the vendor, sanitization result, evidence location, and final destination.
Before closing the case, ITAM reconciles the CI with the external evidence and relevant financial or software records. A configured report can flag missing evidence references, unresolved ownership, or lifecycle states that require investigation.
The closure condition: the asset's technical retirement, authorized physical disposition, and supporting records agree. If the vendor receipt or sanitization validation is missing, the case remains open until the exception is resolved.